
Shawn Freeman
CEO

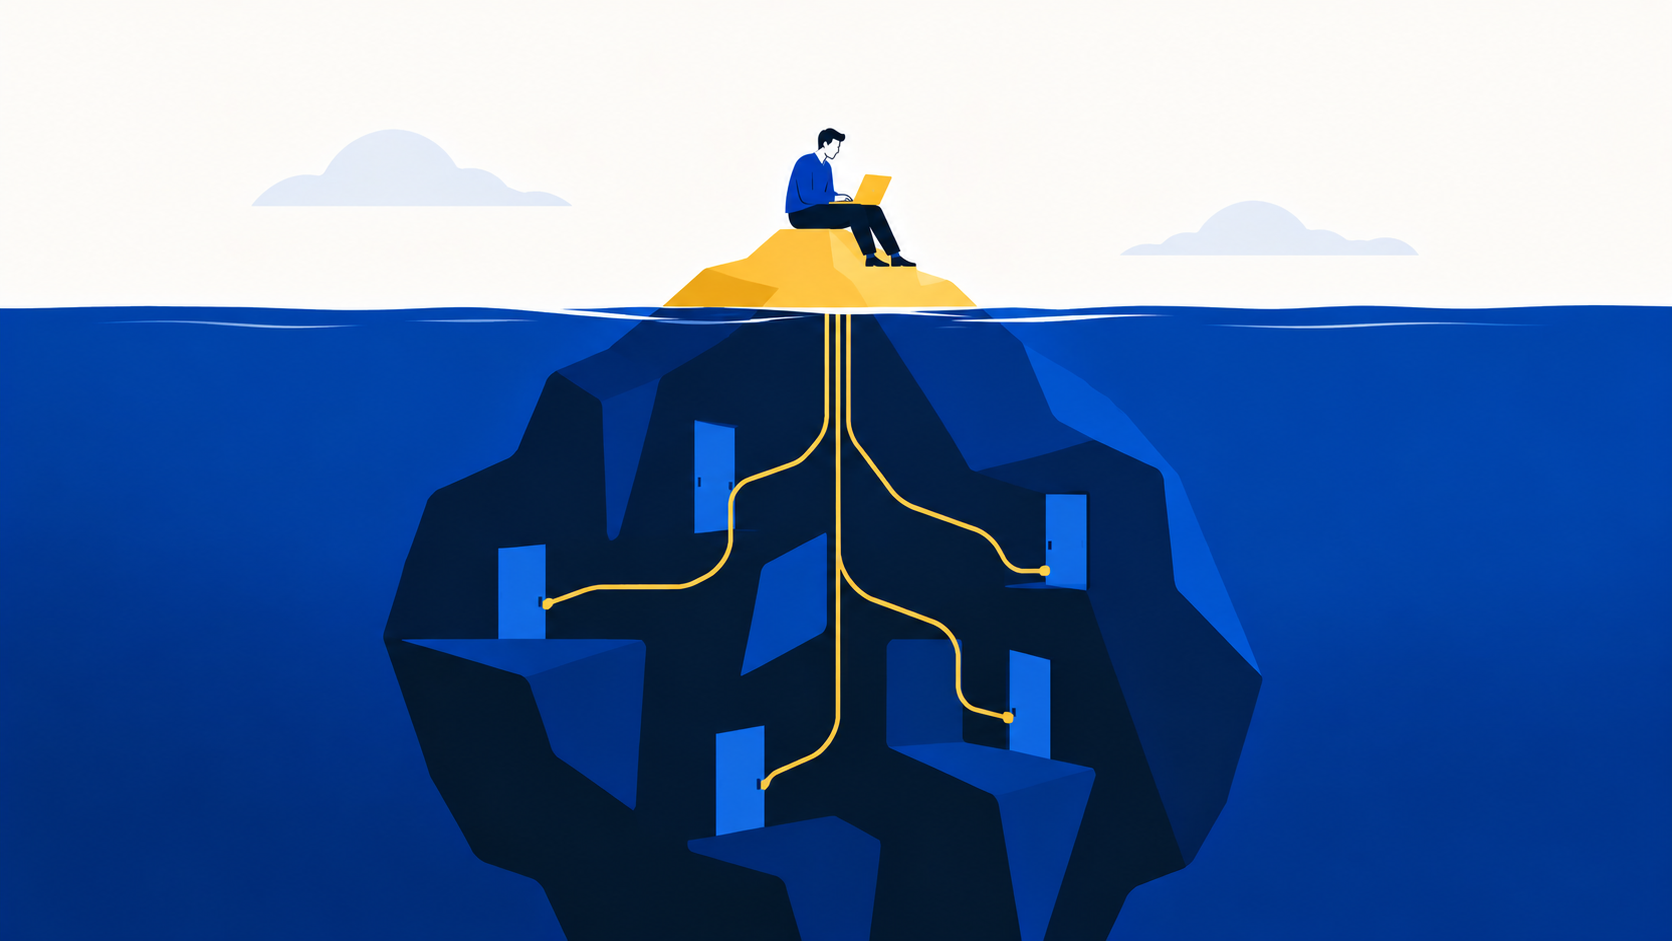
A business owner told us recently about the offshore developers he had brought on. Good people, strong work, a fraction of what he would pay locally. He mentioned almost in passing that they were working from their own computers, in their own homes, several time zones away. Nothing had gone wrong. That was the part that had started to bother him.
Hiring offshore is normal now. A Calgary company with fifteen staff can have a bookkeeper in Manila, a developer in Lahore and a designer in Bogota by the end of the month, and most of the time it works well. What usually does not get updated is the security model underneath it. The contractor gets a Microsoft 365 account, a password, maybe a VPN, and then works on a computer nobody at your company has ever seen or will ever touch.
Two things changed over the past eighteen months that make this worth a second look. Breaches involving a third party nearly doubled. And Canadian federal agencies started warning businesses that some remote IT contractors are not who they claim to be. This post covers what you are actually exposed to, what Canadian privacy law expects of you, what your insurer is quietly asking, and the four realistic ways to close the gap.
Most Canadian small and mid-sized businesses treat an offshore contractor like an employee who happens to live far away. Same accounts, same file access, same shared drives. The difference is that an employee in Calgary is sitting at a company laptop you bought, patched, encrypted and can wipe remotely. The contractor is sitting at a machine you have never inventoried.
That distinction used to be a footnote. It is now the main event. The 2026 Verizon Data Breach Investigations Report found that third parties were involved in 48 percent of breaches, up 60 percent from the year before, after that figure had already doubled the year prior. Your own network can be tidy and still be the second domino.
💡 This is not an argument against offshore contracting. Plenty of well-run Canadian businesses use offshore teams safely. The argument is that access should be designed deliberately rather than inherited from whatever was convenient during onboarding.
When a contractor works from a personal device, every assumption your security program makes about endpoints stops being true. You are not being pessimistic about the person. You are being accurate about the machine.
🚨 Offboarding is where this bites hardest. On the day a contract ends you can disable the account, rotate the passwords and revoke the tokens. You cannot reach into a computer on another continent and remove the eighteen months of client files already sitting on its hard drive.
The useful mental shift is this. The goal is not to secure the contractor's computer, because you never will. The goal is to stop your data from landing on it in the first place.
This is the part that has moved fastest, and it is the reason the topic has gone from an IT preference to a board-level concern.
In July 2025, the RCMP, Public Safety Canada, Global Affairs Canada, FINTRAC and the Canadian Centre for Cyber Security issued a joint advisory warning Canadian businesses that IT workers deployed by the North Korean government pose as legitimate freelancers based in other countries. The advisory singled out smaller organizations, noting that small businesses and start-ups are more attractive targets precisely because they need qualified, affordable labour and rarely have dedicated screening resources. In July 2026, Canada joined ten allied countries in a further alert describing these workers as an insider threat.
The scale is not trivial. The US Treasury sanctioned facilitators of these networks in March 2026, noting they generated close to US$800 million in 2024. Threat research from IBM X-Force and Flare published the same month described the operation in detail, including fabricated LinkedIn profiles, scripted interview preparation and Western collaborators recruited to pass background checks. The RCMP advisory warns that these workers may insert passive malware and backdoors into code, creating exposure to corporate espionage and data theft.
🚨 For a Canadian business there is a second layer beyond the security risk. Paying one of these workers can carry consequences under Canadian sanctions law. The advisory directs suspected violations to the RCMP National Security Information Network.
A detail worth knowing: shipping a company laptop to a contractor does not prove where they are. These operations run what investigators call laptop farms, where a local accomplice receives company-issued hardware and keeps it running so the actual worker can connect to it remotely from somewhere else. Hardware location and human location are two different facts.
⚠ The red flags the Canadian advisory lists are practical ones: reluctance to appear on live video, rates well below market, requests to be paid in cryptocurrency, and inconsistencies between stated education, work history and documentation. Most of these surface during hiring, which is the cheapest place to catch them.
If your contractor handles customer records, employee files, health information or financial details, PIPEDA still treats that information as yours. Sending it offshore for processing is considered a use of the information rather than a disclosure, which means you generally do not need fresh consent, but you remain accountable for what happens to it.
📋 PIPEDA Principle 4.1.3 in plain terms: you are responsible for personal information in your possession or custody, including information transferred to a third party for processing, and you must use contractual or other means to provide a comparable level of protection while that third party has it.
The phrase that does the work there is "or other means." A contract clause alone has never been the whole answer, and the Office of the Privacy Commissioner made that expectation more concrete in September 2026 with draft guidance on assessing third-party service providers. It asks organizations to identify which jurisdictions personal information will be stored and processed in, and to assess the risks to integrity, security and confidentiality before signing anything. The OPC is accepting comments on that draft until December 2026.
If you serve clients in Quebec, Law 25 adds its own requirements around assessments before information leaves the province. And a practical point that gets missed: a contractor working from a personal device in another country is a cross-border processing arrangement whether or not anyone has ever written it down that way.
Cyber insurance questionnaires have become technical documents. Carriers now ask whether multi-factor authentication is enforced on every remote access path, whether endpoint detection is deployed across all devices that touch company data, and how third-party and contractor access is controlled. Those answers are representations, and after an incident they get read as such.
⚠ The question to take to your broker is simple: when this policy asks about endpoint protection on all devices accessing company data, does that include the personal computers our offshore contractors use? Get the answer in writing before you need it, not after.
Misrepresenting a control, even unintentionally, is one of the most common reasons claims are reduced or denied. If you answered yes to comprehensive endpoint coverage while six contractors work from unmanaged personal machines, that gap is worth closing now rather than discovering it during a claim.
There is no single right answer. The right answer depends on how sensitive the data is, how long the engagement runs, and how good the contractor's internet connection is. Here is an honest comparison.
For most Canadian businesses we work with, the cloud desktop is the one that changes the picture most. The contractor connects from whatever computer they own, but the session, the files and the applications live in your environment. Nothing is downloaded. When the engagement ends, the desktop is deleted and the data was never anywhere else. It also gives you something the other options do not: a complete record of what happened during that engagement.
💡 Latency is the one thing to test before committing. A cloud desktop hosted in a Canadian region and accessed from Southeast Asia will feel different than one accessed from Ontario. This is worth piloting with one contractor for two weeks before rolling it out to a team.
Always Beyond scopes, deploys and manages these environments, including the conditional access rules, the session restrictions that stop copy and download, and the provisioning process that gets a new contractor working on day one and fully removed on the last day.
You do not need to solve all of this at once. In order of value per hour spent:
✅ Steps one through four can usually be done in an afternoon and will tell you more about your real exposure than any assessment questionnaire.
Yes, with structure. The risk is not the country someone lives in, it is uncontrolled access from a device you cannot see. Businesses that verify identity properly, give contractors a controlled environment to work in and remove access cleanly at the end get the cost benefit without carrying the exposure.
A contract matters, and you should have one. It is not sufficient on its own. PIPEDA asks for contractual or other means of providing comparable protection, and an agreement cannot be enforced against someone whose real identity you never confirmed, or recover files from a computer in another jurisdiction.
It is a monthly per-user subscription, priced by how much processing power and storage the role needs, so a bookkeeper costs less than a developer. For short or variable engagements, consumption-based virtual desktops are often cheaper than a fixed monthly Cloud PC. Always Beyond can size this against your actual roles rather than a list price.
The signals appear during hiring: avoidance of live video, a rate noticeably below market, payment requested in cryptocurrency, an address or bank account that does not match the stated location, and reference contacts that only exist as email addresses supplied by the candidate. After onboarding it becomes much harder, which is why verification belongs at the front of the process.
A VPN authenticates the connection, not the device. It lets an unmanaged computer onto your network and generally grants broad access once connected. It does nothing to stop files being copied locally. Modern access controls verify the user, the device posture and the specific application being reached, on every request.
The accountability under PIPEDA sits with you either way. Ask the agency who specifically works on your account, what devices they use, how they verify their own people, and what happens to your data when someone rotates off. If they cannot answer clearly, that is useful information.
Not sure what your offshore contractors can actually reach? Always Beyond reviews external and contractor access across your environment, then designs and deploys the access model that fits each role, from conditional access policies through to fully managed cloud desktops. Reach out to start the conversation.
See exactly how your current IT setup measures up to our Hack Free standards. Enter your business email to receive:
